

Guaranteed Accomplishment with Newest May-2026 FREE Fortinet NSE7_SSE_AD-25
Use Valid New Free NSE7_SSE_AD-25 Exam Dumps & Answers
Fortinet NSE7_SSE_AD-25 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 31
Which two additional features does FortiClient integration provide with FortiSASE, when compared to secure web gateway (SWG) deployment? (Choose two.)
- A. inline-CASB protection
- B. SSL inspection
- C. vulnerability management
- D. device posture check
Answer: C,D
Explanation:
When FortiClient is integrated with FortiSASE, it enables vulnerability management and device posture checks, allowing for advanced endpoint compliance enforcement - capabilities not available in standalone secure web gateway (SWG) deployments.
NEW QUESTION # 32
Refer to the exhibits.
A FortiSASE administrator has configured an antivirus profile in the security profile group and applied it to the internet access policy. Remote users are still able to download the eicar.com-zip file from https://eicar.org.
Which configuration on FortiSASE is allowing users to perform the download? (Choose one answer)
- A. Intrusion prevention is disabled.
- B. Deep inspection is not enabled.
- C. Web filter is allowing the URL.
- D. Application control is exempting all the browser traffic.
Answer: B
Explanation:
The core of the issue shown in the exhibits is the lack of visibility into encrypted traffic.
* HTTPS Encryption: The eicar.org website uses the HTTPS protocol for its downloads. This means the data payload, including the test malware file, is encrypted as it traverses the network.
* SSL Inspection Modes: As seen in the Security profile group exhibit (image_5705fc.jpg), the SSL inspection mode is explicitly set to Certificate inspection mode.
* Visibility Gap: Certificate inspection only analyzes the initial SSL handshake, such as the server certificate and SNI (Server Name Indication). It does not decrypt the traffic payload. Consequently, the antivirus engine in FortiSASE cannot "see" or scan the eicar.com-zip file hidden within the encrypted session.
* Resolution Requirement: To detect and block malicious files over HTTPS, SSL Deep Inspection must be enabled. Deep inspection allows FortiSASE to act as a proxy, decrypting the traffic for full content scanning by the antivirus and IPS engines before re-encrypting it for the endpoint.
* Log Analysis: While the web filtering logs (image_5704e5.jpg) show the traffic is "Allowed" because the URL is not blocked by a web filter category, this is only the first step of inspection. The antivirus engine is present but ineffective because it is blind to the encrypted content due to the lack of deep inspection.
NEW QUESTION # 33
An administrator must restrict endpoints from certain countries from connecting to FortiSASE. Which configuration can achieve this? (Choose one answer)
- A. Source IP anchoring to restrict access from the specified countries
- B. Geofencing to restrict access from the required countries
- C. A network lockdown policy on the endpoint profiles
- D. A geography address object as the source for a deny policy
Answer: B
Explanation:
To restrict endpoints from certain countries from connecting to FortiSASE, the administrator should configure Geofencing. This feature provides granular control over which geographic locations are permitted or denied access to the SASE infrastructure.
Geofencing in FortiSASE
Geofencing is the primary mechanism for controlling remote user connectivity based on their origin.
* Functionality: It uses a geography-to-IP mapping database to identify the location of incoming connection requests.
* Access Modes: Administrators can choose between two main modes:
* Allow: Only users from specified countries can connect; all others are blocked.
* Deny: Users from specified countries are blocked; all others are allowed.
* Configuration Path: In the FortiSASE GUI, navigate to Configuration > Geofencing to enable the feature and add the relevant countries.
* Enforcement: Once enabled, the system automatically creates "local-in" policies to drop or permit traffic at the edge of the SASE PoPs before it can consume resources or attempt authentication.
NEW QUESTION # 34
Which authentication method overrides any other previously configured user authentication on FortiSASE?
- A. Local
- B. RADIUS
- C. SSO
- D. MFA
Answer: C
Explanation:
Single Sign-On (SSO) overrides any other previously configured user authentication method on FortiSASE, taking precedence for user authentication.
NEW QUESTION # 35
An existing Fortinet SD-WAN customer is reviewing the FortiSASE ordering guide to identify which add-on is needed to allow future FortiSASE remote users to reach private resources. Which add-on should the customer consider to allow private access? (Choose one answer)
- A. FortiSASE Branch On-Ramp add-on
- B. FortiSASE Dedicated Public IP Address add-on
- C. FortiSASE Global add-on
- D. FortiSASE SPA add-on
Answer: D
Explanation:
To enable remote users to access internal applications located behind an existing FortiGate SD-WAN hub, the customer must license the FortiSASE Secure Private Access (SPA) add-on.
* Secure Private Access (SPA) Use Case: This specific add-on is designed to extend the Fortinet Security Fabric into the SASE cloud, allowing for a hub-and-spoke architecture where the FortiSASE PoPs act as spokes and the customer's on-premises FortiGate acts as the hub.
* Licensing Requirements: The SPA add-on is a per-hub (per service connection) license. It provides the necessary entitlements to establish IPsec tunnels and BGP peering between the SASE infrastructure and the corporate FortiGate.
* Feature Enablement: Once the SPA license is applied, the Configuration > Private Access menu becomes available in the FortiSASE portal. This allows administrators to define "Service Connections" to their private data centers or cloud VPCs.
* Analysis of Other Options:
* Option A: The Global add-on is typically related to expanding the geographic reach or performance of the SASE PoPs, not specifically for private resource routing.
* Option B: The Branch On-Ramp refers to connecting physical office locations (Thin Edge) to SASE, rather than the specific licensing for private application access for remote users.
* Option D: Dedicated Public IP Address is used for source IP anchoring (SIA) to ensure remote users egress with a consistent IP for third-party SaaS IP-whitelisting.
NEW QUESTION # 36
Refer to the exhibits.
How will the application vulnerabilities be patched, based on the exhibits provided? (Choose one answer)
- A. The vulnerability will be patched by installing the patch from the vendor's website.
- B. An administrator will patch the vulnerability remotely using FortiSASE.
- C. The vulnerability will be patched automatically based on the endpoint profile configuration.
- D. The end user will patch the vulnerabilities using the FortiClient software.
Answer: B
Explanation:
Based on the settings shown in the provided exhibits, the vulnerability remediation workflow is determined by the Endpoint Profile and the Vulnerability Dashboard.
* Endpoint Profile Evaluation: The top exhibit displays the Scan for Vulnerabilities settings. The toggle for Automatically patch vulnerabilities is explicitly set to Disabled. Consequently, the system will not perform automated remediation when a scan completes.
* Manual Patching Requirement: The Vulnerability Dashboard (bottom exhibit) lists several application vulnerabilities with a Patching status of Manual patching required. In a FortiSASE environment, "Manual" indicates that the vulnerability cannot be handled by the client's autonomous update process and requires a direct instruction from the management plane.
* Administrative Intervention: The dashboard includes a Patch endpoints action button. Since auto- patching is disabled in the profile, an administrator must manually select the vulnerabilities and click the "Patch endpoints" button to remotely trigger the patching sequence on the managed endpoints via the FortiSASE cloud service.
* Workflow Logic: While FortiClient acts as the "conductor" on the local machine to facilitate the download and installation, the trigger for this specific scenario is the administrator's remote action within the portal. This differentiates it from Option D (which is disabled) and Option C (which would involve a user manually browsing a website outside the managed SASE workflow).
NEW QUESTION # 37
For monitoring potentially unwanted applications on endpoints, which information is available on the FortiSASE software installations page?
- A. the vendor of the software
- B. the license status of the software
- C. the endpoint the software is installed on
- D. the usage frequency of the software
Answer: C
Explanation:
The FortiSASE software installations page shows which endpoints have specific software installed, allowing administrators to monitor potentially unwanted applications across the network.
NEW QUESTION # 38
Which secure internet access (SIA) use case minimizes individual workstation or device setup, because you do not need to install FortiClient on endpoints or configure explicit web proxy settings on web browser-based end points?
- A. SIA for SSLVPN remote users
- B. SIA for agentless remote users
- C. SIA for inline-CASB users
- D. SIA for site-based remote users
Answer: B
Explanation:
The Secure Internet Access (SIA) use case that minimizes individual workstation or device setup is SIA for agentless remote users. This use case does not require installing FortiClient on endpoints or configuring explicit web proxy settings on web browser-based endpoints, making it the simplest and most efficient deployment.
* SIA for Agentless Remote Users:
* Agentless deployment allows remote users to connect to the SIA service without needing to install any client software or configure browser settings.
* This approach reduces the setup and maintenance overhead for both users and administrators.
* Minimized Setup:
* Without the need for FortiClient installation or explicit proxy configuration, the deployment is straightforward and quick.
* Users can securely access the internet with minimal disruption and administrative effort.
References:
FortiOS 7.6 Administration Guide: Details on different SIA deployment use cases and configurations.
FortiSASE 23.2 Documentation: Explains how SIA for agentless remote users is implemented and the benefits it provides.
NEW QUESTION # 39
During FortiSASE provisioning, how many security points of presence (POPs) need to be configured by the FortiSASE administrator?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
Explanation:
During initial provisioning, you can select fewer security sites than the maximum you are entitled to. In this case, upon each login, the FortiSASE portal prompts you to select up to the maximum number of security sites. If you add additional security sites using this prompt, then FortiSASE allows for increasing the number of security sites without FortiCare Support. FortiSASE may experience up to 10 minutes of downtime when you apply the entitlement. If any errors occur, FortiSASE cannot automatically rollback without FortiCare Support. For provisioning, you must select a minimum of two security sites for redundancy.
https://docs.fortinet.com/document/fortisase/latest/administration-guide/751044/appendix-a- fortisase-data-centers#Number
NEW QUESTION # 40
Refer to the exhibits. A FortiSASE administrator has configured an antivirus profile in the security profile group and applied it to the internet access policy. Remote users are still able to download the eicar.com-zip file from https://eicar.org.
Which configuration on FortiSASE is allowing users to perform the download?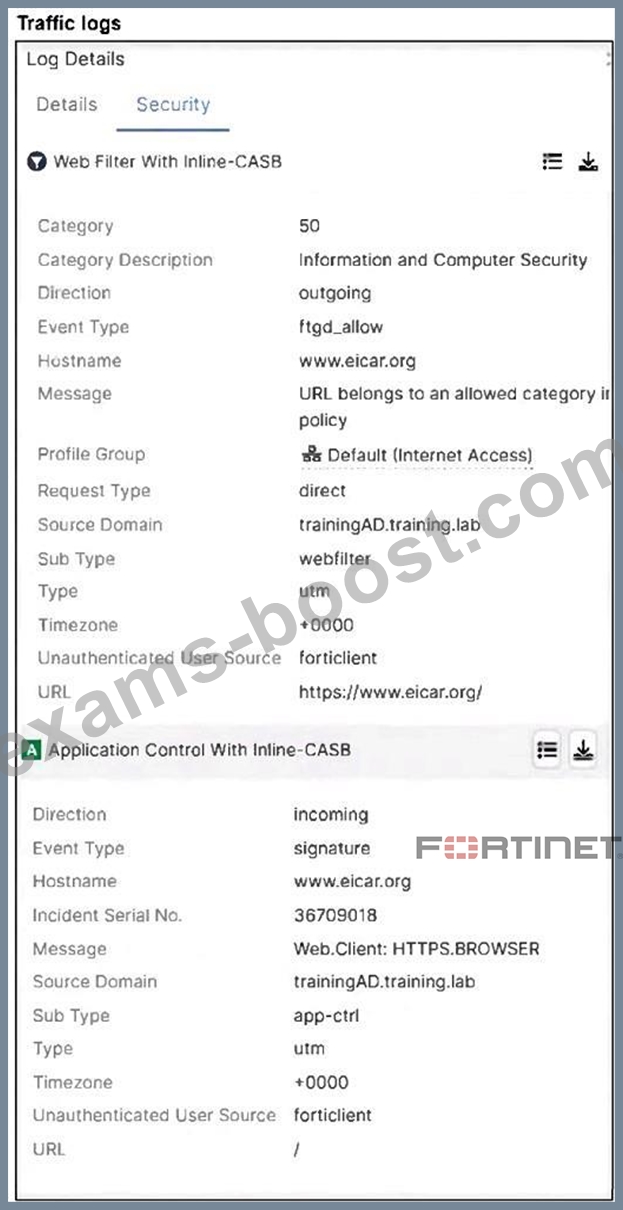

- A. Intrusion prevention is disabled.
- B. Deep inspection is not enabled.
- C. Web filter is allowing the URL.
- D. Application control is exempting all the browser traffic.
Answer: B
Explanation:
The SSL inspection mode is set to certificate inspection, which only inspects SSL/TLS headers and does not allow full scanning of encrypted content. Without full (deep) inspection, the antivirus profile cannot scan or block malicious files (like eicar.com-zip) delivered over HTTPS, allowing the download to proceed.
NEW QUESTION # 41
An administrator must restrict endpoints from certain countries from connecting to FortiSASE.
Which configuration can achieve this?
- A. Configure a network lockdown policy on the endpoint profiles.
- B. Configure source IP anchoring to restrict access from the specified countries.
- C. Configure geofencing to restrict access from the required countries.
- D. Configure a geography address object as the source for a deny policy.
Answer: C
Explanation:
Geofencing allows the administrator to restrict or allow access to FortiSASE services based on the geographic location of the endpoints, effectively blocking connections from specified countries.
NEW QUESTION # 42
Which two are required to enable central management on FortiSASE? (Choose two.)
- A. The FortiManager IP address in the FortiSASE central management configuration.
- B. FortiSASE central management entitlement applied to FortiManager.
- C. FortiSASE connector configured on FortiManager.
- D. FortiManager and FortiSASE registered under the same FortiCloud account.
Answer: C,D
Explanation:
To enable central management, FortiManager must have a FortiSASE connector configured, and both FortiSASE and FortiManager must be registered under the same FortiCloud account to establish trust and synchronization.
NEW QUESTION # 43
Refer to the exhibits. How will the application vulnerabilities be patched, based on the exhibits provided?

- A. The vulnerability will be patched by installing the patch from the vendor's website.
- B. An administrator will patch the vulnerability remotely using FortiSASE.
- C. The vulnerability will be patched automatically based on the endpoint profile configuration.
- D. The end user will patch the vulnerabilities using the FortiClient software.
Answer: B
Explanation:
The "Automatically patch vulnerabilities" option is disabled in the endpoint profile. Additionally, the Vulnerability Dashboard shows the patching status as "Manual patching required." This means an administrator must manually initiate the patching process remotely using FortiSASE.
NEW QUESTION # 44
When deploying FortiSASE agent-based clients, which three features are available compared to an agentless solution? (Choose three.)
- A. ZTNA tags
- B. Anti-ransomware protection
- C. Vulnerability scan
- D. Web filter
- E. SSL inspection
Answer: C,D,E
Explanation:
When deploying FortiSASE agent-based clients, several features are available that are not typically available with an agentless solution. These features enhance the security and management capabilities for endpoints.
* Vulnerability Scan:
* Agent-based clients can perform vulnerability scans on endpoints to identify and remediate security weaknesses.
* This proactive approach helps to ensure that endpoints are secure and compliant with security policies.
* SSL Inspection:
* Agent-based clients can perform SSL inspection to decrypt and inspect encrypted traffic for threats.
* This feature is critical for detecting malicious activities hidden within SSL/TLS encrypted traffic.
* Web Filter:
* Web filtering is a key feature available with agent-based clients, allowing administrators to control and monitor web access.
* This feature helps enforce acceptable use policies and protect users from web-based threats.
References:
FortiOS 7.6 Administration Guide: Explains the features and benefits of deploying agent-based clients.
FortiSASE 23.2 Documentation: Details the differences between agent-based and agentless solutions and the additional features provided by agent-based deployments.
NEW QUESTION # 45
In a FortiSASE secure web gateway (SWG) deployment, which two features protect against web- based threats? (Choose two.)
- A. SSL deep inspection for encrypted web traffic
- B. intrusion prevention system (IPS) for web traffic
- C. malware protection with sandboxing capabilities
- D. web application firewall (WAF) for web applications
Answer: A,C
Explanation:
SSL deep inspection allows FortiSASE to analyze encrypted web traffic for threats, while malware protection with sandboxing detects and blocks malicious files delivered through web channels.
NEW QUESTION # 46
Which policy type is used to control traffic between the FortiClient endpoint to FortiSASE for secure internet access?
- A. private access policy
- B. secure web gateway (SWG) policy
- C. thin edge policy
- D. VPN policy
Answer: B
Explanation:
The Secure Web Gateway (SWG) policy is used to control traffic between the FortiClient endpoint and FortiSASE for secure internet access. SWG provides comprehensive web security by enforcing policies that manage and monitor user access to the internet.
* Secure Web Gateway (SWG) Policy:
* SWG policies are designed to protect users from web-based threats and enforce acceptable use policies.
* These policies control and monitor user traffic to and from the internet, ensuring that security protocols are followed.
* Traffic Control:
* The SWG policy intercepts all web traffic, inspects it, and applies security rules before allowing or blocking access.
* This policy type is crucial for providing secure internet access to users connecting through FortiSASE.
References:
FortiOS 7.6 Administration Guide: Details on configuring and managing SWG policies.
FortiSASE 23.2 Documentation: Explains the role of SWG in securing internet access for endpoints.
NEW QUESTION # 47
Refer to the exhibits. Jumpbox and Windows-AD are endpoints from the same remote location.
Jumpbox can access the internet through FortiSASE, while Windows-AD can no longer access the internet.
Based on the information in the exhibits, which reason explains the outage on Windows-AD?


- A. The device posture for Windows-AD has changed.
- B. The FortiClient version installed on Windows AD does not match the expected version on FortiSASE.
- C. The remote VPN user on Windows-AD no longer matches any VPN policy.
- D. Windows-AD is excluded from FortiSASE management.
Answer: A
Explanation:
The Windows-AD endpoint now has both "FortiSASE-Compliant" and "FortiSASE-Non- Compliant" tags due to failing the antivirus software check. As a result, the Secure Internet Access Policy matches the "Non-Compliant" rule, which is set to Deny, causing the device to lose internet access.
NEW QUESTION # 48
What is required to enable the MSSP feature on FortiSASE? (Choose one answer)
- A. Role-based access control (RBAC) must be assigned to identity and access management (IAM) users using the FortiCloud IAM portal.
- B. MSSP user accounts and permissions must be configured on the FortiSASE portal.
- C. The MSSP add-on license must be applied to FortiSASE.
- D. Multi-tenancy must be enabled on the FortiSASE portal.
Answer: A
Explanation:
To enable the Managed Security Service Provider (MSSP) feature on FortiSASE, the administrative framework must be established outside of the local SASE instance within the broader FortiCloud ecosystem.
* FortiCloud IAM Integration: The FortiSASE MSSP portal relies on FortiCloud Identity & Access Management (IAM) to define the scope of management for internal teams. Administrators do not create local "MSSP users" within the SASE portal itself; instead, they must use the FortiCloud IAM portal to assign specific Role-Based Access Control (RBAC) to IAM users.
* Permissions and Scope: These RBAC settings determine which customer tenants (Organizational Units or OUs) an MSSP administrator can view, configure, or monitor. Without the proper role assignment in the IAM portal, the MSSP portal and its multi-tenant viewing capabilities will not be accessible to the user, even if the account has the necessary licenses.
* Hierarchical Management: Once RBAC is correctly assigned, the MSSP administrator can leverage the FortiCloud Organizations service to manage multiple customer accounts from a single pane of glass. This centralized approach ensures that security policies and configurations can be standardized across the entire customer base while maintaining strict data isolation between tenants.
According to the FortiSASE 25 Multitenant Deployment Guide, configuring the IAM portal is the primary prerequisite that grants an MSSP internal team the permissions necessary to perform operations on customer FortiSASE tenants.
NEW QUESTION # 49
When viewing the daily summary report generated by FortiSASE. the administrator notices that the report contains very little data. What is a possible explanation for this almost empty report?
- A. There are no security profile group applied to all policies.
- B. The web filter security profile is not set to Monitor
- C. Digital experience monitoring is not configured.
- D. Log allowed traffic is set to Security Events for all policies.
Answer: D
Explanation:
If the daily summary report generated by FortiSASE contains very little data, one possible explanation is that the "Log allowed traffic" setting is configured to log only "Security Events" for all policies. This configuration limits the amount of data logged, as it only includes security events and excludes normal allowed traffic.
* Log Allowed Traffic Setting:
* The "Log allowed traffic" setting determines which types of traffic are logged.
* When set to "Security Events," only traffic that triggers a security event (such as a threat detection or policy violation) is logged.
* Impact on Report Data:
* If the log setting excludes regular allowed traffic, the amount of data captured and reported is significantly reduced.
* This results in reports with minimal data, as only security-related events are included.
References:
FortiOS 7.6 Administration Guide: Provides details on configuring logging settings for traffic policies.
FortiSASE 23.2 Documentation: Explains the impact of logging configurations on report generation and data visibility.
NEW QUESTION # 50
Which FortiSASE feature ensures least-privileged user access to corporate applications that are protected by an on-premises FortiGate device?
- A. zero trust network access (ZTNA)
- B. cloud access security broker (CASB)
- C. remote browser isolation (RBI)
- D. secure web gateway (SWG)
Answer: A
Explanation:
ZTNA enforces least-privileged access by verifying user identity and device posture before granting access to specific corporate applications, even when protected by an on-premises FortiGate.
NEW QUESTION # 51
Which information can an administrator monitor using reports generated on FortiSASE?
- A. SD-WAN performance
- B. FortiClient vulnerability assessment
- C. sanctioned and unsanctioned Software-as-a-Service (SaaS) applications usage
- D. FortiSASE administrator and system events
Answer: C
Explanation:
FortiSASE reporting provides visibility into the usage of sanctioned and unsanctioned SaaS applications, enabling administrators to monitor cloud application activity and enforce security policies.
NEW QUESTION # 52
A Fortinet customer is considering integrating FortiManager with FortiSASE. What are two prerequisites they should consider? (Choose two answers)
- A. Adding a FortiManager connection add-on license to FortiSASE.
- B. Placing FortiManager in the same FortiCloud account as FortiSASE.
- C. Reducing the number of FortiSASE PoPs that support FortiManager.
- D. Running a FortiManager version that is supported by FortiSASE.
Answer: B,D
Explanation:
Integrating FortiManager with FortiSASE allows for central management of configuration objects like addresses and5 security 6profiles. For this integration to function correctly, the following key prerequisites must be met:
* Same FortiCloud Account: A fundamental requirement for the integration is that both 10the FortiSASE instance and the FortiManager (whether physical, VM, or Cloud) must be registered under the same FortiCloud (FortiCare) account. This common identity allows the platforms to securely discover and authorize each other for synchronization.
* Supported Firmware Version: The FortiManager must run a firmware version that is compatible with the FortiSASE release. According to the FortiSASE 25 Enterprise Administrator Study Guide, FortiManager version 7.4.4 or later is generally required to support the specific API connectors and object synchronization logic used by current FortiSASE environments. Using an unsupported version may result in synchronization failures or missing configuration features.
* Management Logic: Once these prerequisites are met, the administrator can enable "Central Management" in the FortiSASE portal. This creates a one-way synchronization where FortiManager acts as the source of truth for objects like Security Profile Groups, ensuring consistent security posture across both the SASE cloud and on-premises FortiGates.
NEW QUESTION # 53
What is the role of ZTNA tags in the FortiSASE Secure Internet Access (SIA) and Secure Private Access (SPA) use cases? (Choose one answer)
- A. ZTNA tags are created to isolate browser sessions in SIA and enforce data loss prevention in SPA for all devices.
- B. ZTNA tags determine device posture for endpoints running FortiClient and are used to grant or deny access in SIA or SPA based on that posture.
- C. ZTNA tags determine device posture for non-web traffic protocols and are applied only in agentless deployments for SIA.
- D. ZTNA tags are applied to unmanaged endpoints without FortiClient to secure HTTP and HTTPS traffic in SIA and SPA.
Answer: B
Explanation:
In the Fortinet SASE architecture, Zero Trust Network Access (ZTNA) tags (which have been renamed to Security Posture Tags starting with FortiClient/EMS 7.4.0) play a critical role in continuous posture assessment. These tags are dynamic metadata assign8ed to an endpoint based on specific conditions or
"tagging rules" defined in the FortiSASE Endpoint Management Service (EMS).
* Posture Determination: The FortiClient agent, installed on the endpoint, monitors the device for various security attributes-such as whether an antivirus is running, the presence of specific registry keys, OS version, or the absence of critical vulnerabilities.
* SIA (Secure Internet Access) Use Case: In SIA scenarios, FortiSASE uses these tags within security policies to control internet access. For example, a policy may allow full internet access only to endpoints tagged as "Compliant" while redirecting "Non-Compliant" devices to a restricted remediation portal.
* SPA (Secure Private Access) Use Case: In SPA (specifically ZTNA Proxy mode), the tags are synchronized from FortiSASE to the corporate FortiGate (acting as the ZTNA Access Proxy).12 When a user attempts to access a private application, the FortiGate checks the endpoint's client certificate and its synchronized ZTNA tags.13 If the endpoint does not meet the required posture (e.g., it is missing a required "Domain-Joined" tag), access is denied at the session level.
According to the FortiSASE 25 Enterprise Administrator Study Guide, ZTNA tags are fundamental to the
"Zero Trust" principle because they move beyond static identity (username/password) to verify the real-time security state of the device before granting access to either the internet or internal private resources.
NEW QUESTION # 54
......
NSE7_SSE_AD-25 Braindumps PDF, Fortinet NSE7_SSE_AD-25 Exam Cram: https://testking.exams-boost.com/NSE7_SSE_AD-25-valid-materials.html